A role-based permission system for an existing coaching SaaS, letting organisations edit team members' development plans safely — without breaking ownership.
This engagement implemented a structured organisation-level permission system for managing Individual Development Plans (IDPs) inside an existing coaching and development SaaS platform. It introduced a scalable permission model so organisation users — coaches or administrators — can view and edit team members' IDPs based on configurable access rules, while ownership stays with the original user.
Coaches and admins can edit team IDPs under configurable, role-based rules.
The platform needed organisations to collaborate on their members' development plans — but existing logic tied editing to ownership, with no safe way to grant coaches or admins controlled edit access.
A scalable permission model was added at the organisation-user layer: a dedicated 'Can edit IDP' toggle grants controlled editing without affecting ownership, with read-only fallbacks, editing indicators, menu-level access routing, and frontend safeguards keeping workflows consistent.
The permission architecture was layered onto the existing organisation-user model, keeping ownership logic intact while adding configurable, role-based editing — with frontend-controlled safeguards for consistency.
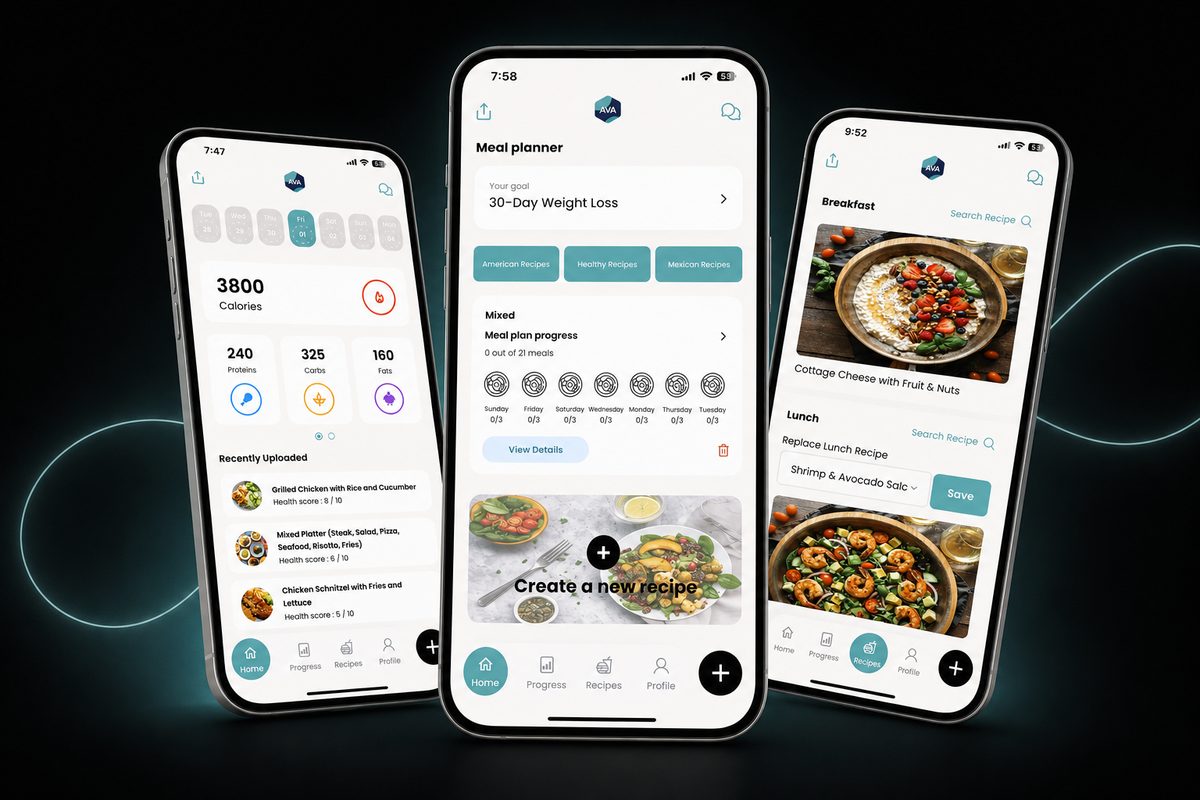
A health and nutrition app that turns weight-loss, muscle-gain, or healthy-living goals into a clear daily plan — calorie and macro tracking, food logging, an AI nutrition assistant, and goal-based meal planning.
Read case study →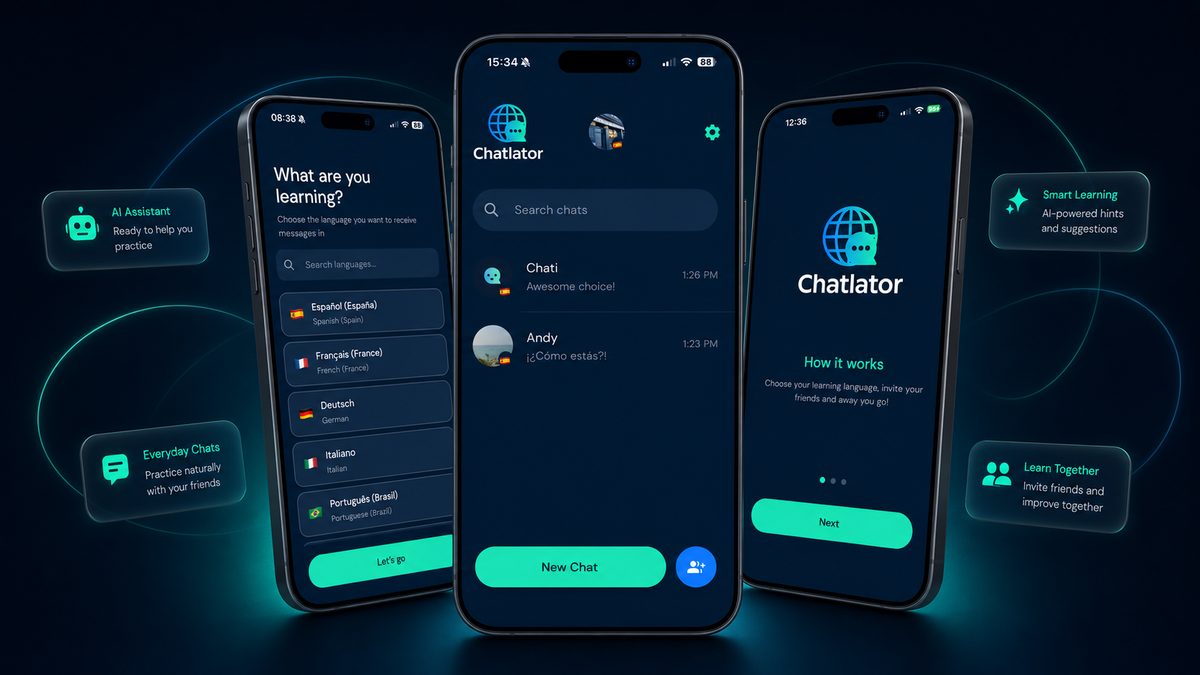
A messenger that turns real chats into language practice: message friends as usual and every message is auto-translated into the language you're learning, with an AI tutor guiding you to fluency.
Read case study →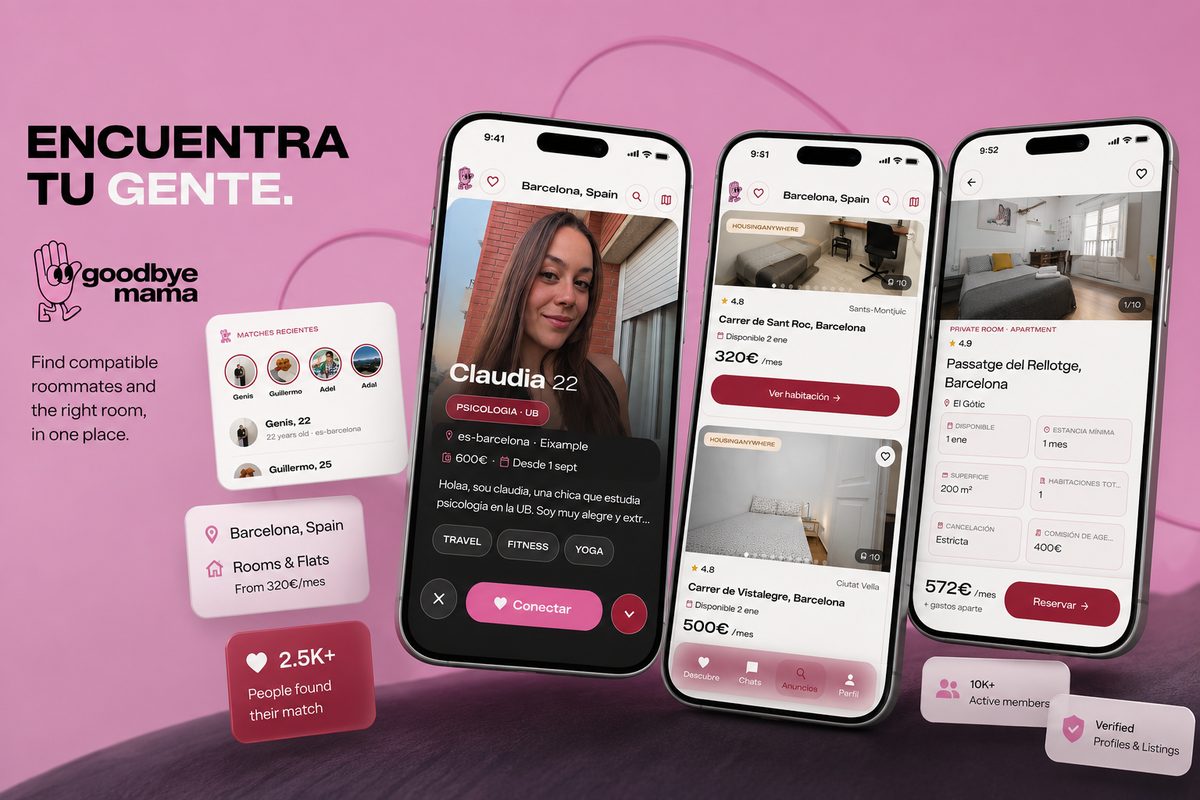
A roommate-matching and room-finding platform — compatibility-based matches, real room and flat listings with booking, and in-app chat, across a mobile app and the web.
Read case study →We design role-based access and collaboration models that scale safely inside existing products. Let's map yours.
Book a Free Strategy Call →3-week launch · Fixed pricing · Senior team